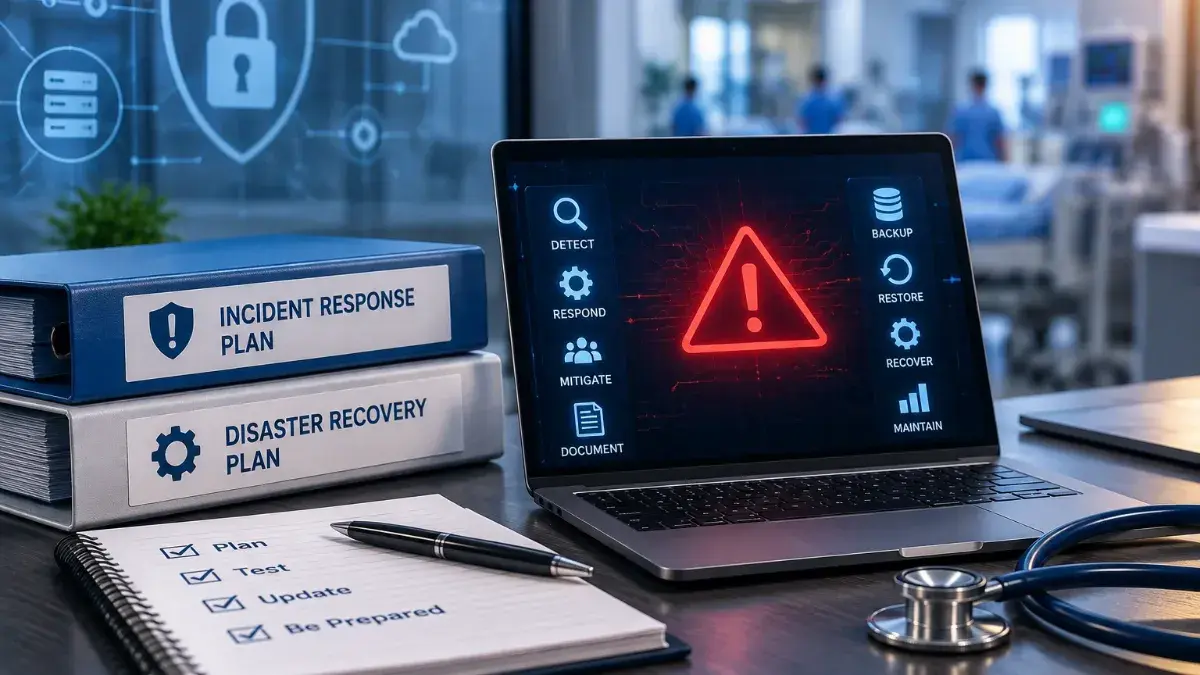
Most healthcare organizations hope they never have to put their incident response or disaster recovery plans into action.
But hope is not a recovery strategy.
When a cyberattack, system outage, natural disaster, or other disruption occurs, the middle of an incident is not the time to discover that responsibilities are unclear, backups cannot be restored quickly, or critical systems were never prioritized.
That is one of the important themes behind the proposed changes to the HIPAA Security Rule. If finalized, the proposal would establish more specific expectations around how covered entities and business associates prepare for security incidents, respond when they occur, and restore critical systems afterward.
The bigger takeaway for healthcare organizations is simple: having a plan on paper may no longer be enough. Organizations need to know whether that plan actually works.
Incident Response: From Having a Policy to Being Prepared
Under the current HIPAA Security Rule, organizations must have policies and procedures for identifying and responding to suspected or known security incidents, mitigating harmful effects when possible, and documenting incidents and their outcomes.
The proposed HIPAA Security Rule would add more specific requirements around that process, including a written Security Incident Response Plan outlining how workforce members report suspected or known incidents and how the organization responds.
It would also establish more detailed expectations around testing and revising those plans.
That distinction matters.
A written incident response plan can identify who should be contacted and what steps should be taken. Testing that plan helps determine whether employees know what to do, whether responsibilities are clear, and whether the process can work under the pressure of a real incident.
Download Your Complimentary Incident Response Checklist
Disaster Recovery: What Needs to Come Back First?
Incident response focuses on what happens when a security incident occurs. Disaster recovery asks another critical question: How quickly can your organization get back to normal operations?
The current Security Rule requires a contingency plan that addresses areas such as backing up ePHI, restoring lost data, and continuing critical processes during an emergency.
The proposed rule would make some of those expectations more specific:
If finalized as proposed, organizations would need to establish written procedures for restoring certain critical electronic information systems and data within specified timeframes, including a proposed 72-hour restoration requirement for certain critical systems and data.
Organizations would also need to analyze the criticality of their systems and technology assets. In practical terms, that means understanding which systems the organization depends on most and determining what needs to be restored first.
For a healthcare organization, that exercise can extend beyond compliance. If several systems become unavailable at the same time, leaders should already know which ones are essential to patient care, operations, and the protection of ePHI.
A Plan You Have Never Tested Is Still an Unknown
It is easy to think of incident response and disaster recovery as documents that live inside a compliance program. Their real value becomes apparent when something goes wrong.
Can employees recognize and report a potential security incident?
Does everyone know who is responsible for responding?
Can your organization restore critical data from its backups?
Does your IT provider understand which systems need to be prioritized?
Have you actually tested any of it?
Those are valuable questions regardless of what ultimately happens with the proposed HIPAA Security Rule.
The proposed changes are not final, and current HIPAA requirements remain in effect. But healthcare organizations can use this time to review their incident response and disaster recovery processes, identify gaps, coordinate with their IT providers, and test whether their plans work as expected.
Because when an incident happens, the most valuable plan is not the one sitting in a binder.
It is the one your organization is prepared to execute.
Leave a Reply